Trust You Can Build On: The Assurance Behind TRIDENT
Behind every simple TRIDENT interaction is a national trust infrastructure designed to protect identity, credentials and high-value digital transactions.
Any organisation considering building on TRIDENT eventually asks the same question: can we rely on this?
It's the right question. Connecting a service to shared identity infrastructure means depending on decisions someone else made about security, governance and long term direction. So it's worth being specific about what those decisions were, and what evidence supports them.
Independently evaluated, not self declared
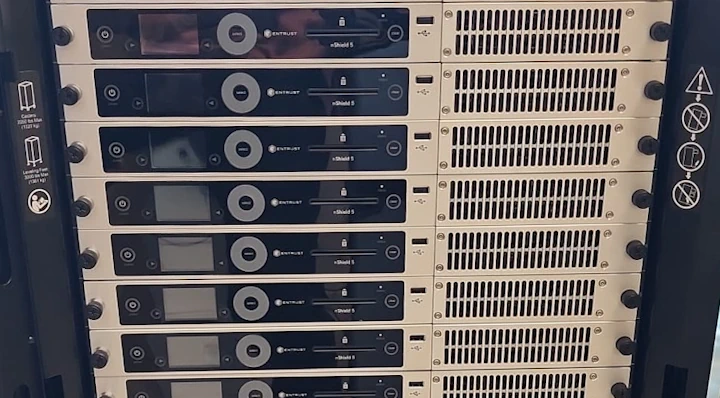
The cryptographic components protecting TRIDENT's national trust infrastructure have been evaluated by accredited independent laboratories, not assessed internally.
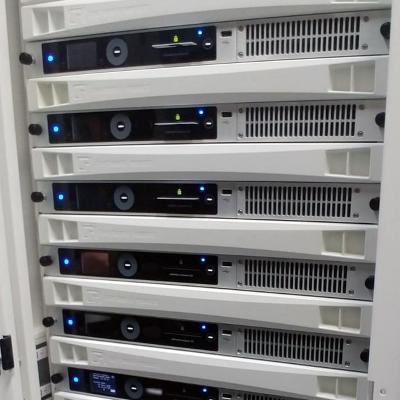
The hardware safeguarding Barbados' root cryptographic material is certified to FIPS 140-3 Level 3 and evaluated under Common Criteria at EAL4+, covering physical tamper resistance, identity based access and key handling. The certificate authority, the validation and timestamping services, and the remote signing activation service each carry their own separate Common Criteria evaluations. These are internationally recognised references, the same class of assessment applied to trust infrastructure operated by governments and financial institutions elsewhere.
Standards you can verify independently
TRIDENT is built on published, open standards from internationally recognised bodies: the World Wide Web Consortium, the Internet Engineering Task Force, the OpenID Foundation and OASIS, which define how the web, secure access and digital identity work; ISO and IEC, the international standards organisations, together with the ITU, the United Nations agency for telecommunications; ETSI and CEN in Europe, whose specifications underpin the European Union's eIDAS framework; ICAO, which sets the global rules for passports and travel documents; and NIST in the United States, whose guidance is widely used for identity assurance and cryptography.
This matters practically. Your team can assess these standards independently, hire against skills that already exist in the market, and avoid depending on any single supplier's implementation. It's also what makes future cross border recognition technically possible, including within the Caribbean, once the corresponding agreements exist.
Decisions that stay in Barbados
Adopting international standards is not the same as adopting external policy. Standards define how trust evidence can be exchanged and validated. They don't decide who gets trusted.
Government retains authority over identity assurance rules, national root certification authorities, credential policies, approval of issuers and verifiers, onboarding of relying parties, recognition of external trust frameworks, and production authorisation. The core trust services are deployed locally, inside Government controlled infrastructure. Participation is approved, not open by default.
Built for the next cryptographic transition
Cryptographic standards evolve. International bodies have set out a migration path toward quantum resistant cryptography running through the next decade, which means systems being built today need to be able to make that transition without being rebuilt.
TRIDENT's cryptographic hardware already supports the post quantum algorithms standardised by NIST, and its architecture allows new algorithms to be introduced through firmware updates rather than hardware replacement. It also supports hybrid certificates that combine classical and post quantum algorithms, which makes a gradual, planned transition possible instead of a single disruptive cut over.
For an integrating organisation, this reduces the likelihood that your integration will need re architecting when migration deadlines arrive.
What you keep, and what you stop rebuilding
Connecting to TRIDENT doesn't transfer responsibility for your service. A ministry still determines eligibility. A bank still applies its own risk and regulatory policies. A licensing authority still decides whether a licence is issued.
What changes is the foundation. Identity verification, authentication, verified data access, digital signing and credential validation become capabilities you connect to, rather than systems you build, certify and maintain yourself.
The Integration Framework provides protected APIs, technical documentation, authorisation mechanisms and controlled testing environments, so integration can start with a single use case and expand as readiness allows. Everything is available through the Integration Portal.
New to TRIDENT's security foundations?
For a plain-language explanation of the national root of trust and how identity is protected, the article Protecting the Foundations of Digital Trust covers the essentials.